
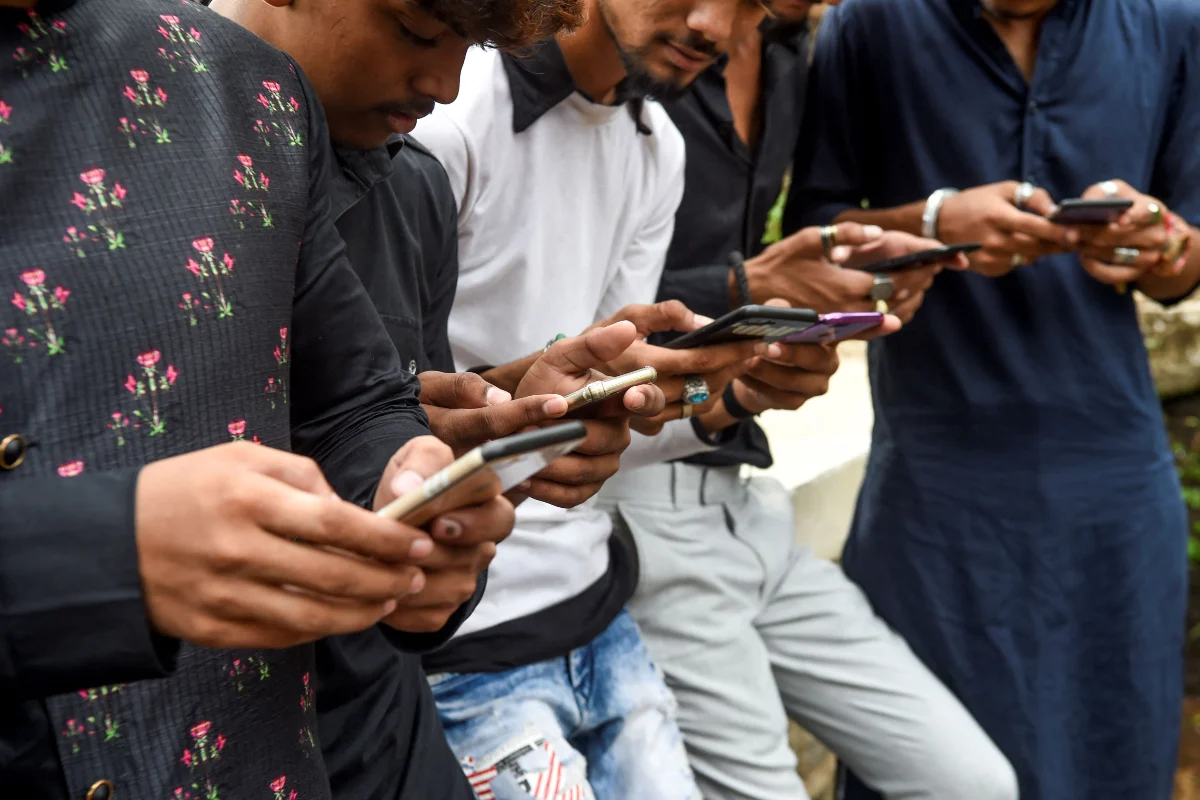
The Telecom Regulatory Authority of India (TRAI) has introduced a significant regulatory shift in the nation’s digital communications landscape, mandating that caller-ID and call-management applications share user-generated spam reports directly with telecom service providers. Under the new amendments to the commercial communications framework, apps that allow users to flag junk calls or messages must now transmit this data to a centralized, blockchain-based ledger maintained by telecom operators. This platform, originally designed to enforce the Telecom Commercial Communications Customer Preference Regulations (TCCCPR), serves as the backbone for India’s anti-spam enforcement.
The move marks a pivotal moment in the ongoing struggle to curb the deluge of unsolicited commercial communications (UCC) that plagues the Indian market. While the regulator maintains that the integration of third-party data is essential to creating a comprehensive "spam shield," the policy has drawn sharp criticism from industry players, most notably Truecaller, the Swedish firm that dominates the Indian caller-ID market with over 350 million active users in the country.
A Chronology of Regulatory Friction
The relationship between India’s telecom regulator and third-party call-management applications has been characterized by intermittent tension over the past several years. The current mandate is the latest in a series of regulatory interventions aimed at reclaiming control over the nation’s telecommunications infrastructure from decentralized apps.
In 2025, the debate intensified when TRAI introduced restrictions preventing third-party apps from automatically flagging or blocking calls originating from government-designated number series. These series, often used for promotional, transactional, and service-related communications, were granted a degree of regulatory immunity. At the time, Truecaller and similar entities argued that this exemption created a "free pass" for spammers, effectively allowing unwanted callers to bypass sophisticated filtering algorithms.
Despite these objections, the latest amendments have not only retained those restrictions but have further tightened the operational scope of these apps. By requiring the sharing of proprietary spam-reporting data, the regulator is effectively absorbing the "intelligence" layer of these apps into the state-sanctioned telecom infrastructure. This transition suggests a shift from a collaborative ecosystem to one where private data is treated as a public utility to be managed by the telecom sector.
Scale of the Spam Epidemic
The urgency behind TRAI’s decision is rooted in the sheer volume of unsolicited traffic hitting the Indian network. According to data released by Truecaller in early 2026, Indian users were subjected to approximately 42 billion spam calls in 2025. This figure encompasses a broad spectrum of activity, including automated robocalls, fraudulent phishing attempts, and aggressive telemarketing campaigns.
Of those 42 billion instances, Truecaller reported that its platform successfully blocked nearly 12 billion calls, providing a critical layer of defense for consumers. This volume highlights why the regulator is eager to tap into the data pools of private apps. If the blockchain-based system managed by telcos can ingest the real-time flagging data from millions of users, the regulator argues that it could theoretically shut down fraudulent numbers at the network level before they even reach the end-user’s device.
However, the efficacy of this strategy remains a subject of intense debate among industry analysts. The technical hurdle lies in the speed of the blockchain system versus the speed of real-time cloud-based filtering. Critics worry that by forcing a "one-way exchange" of data, the regulator may inadvertently stifle the agility of third-party apps, which currently rely on machine learning and community-sourced data to identify spam patterns as they emerge.
Truecaller’s Critique: A Question of Competition
Truecaller has formally labeled the new requirement as "anti-competitive," arguing that the policy mandates the transfer of commercially sensitive and valuable data to telecom operators. For an app like Truecaller, the reputation signals and community reporting mechanisms are core assets that differentiate their service in a crowded market.
By forcing these apps to feed their internal data into the telecom operators’ blockchain, the regulator is essentially compelling private companies to hand over their proprietary intelligence to the very entities—telecom companies—that are often the primary carriers of the spam traffic. This has led to concerns regarding the "level playing field." If telecom operators gain access to the same reputation metrics that drive Truecaller’s blocking success, it could theoretically undermine the competitive advantage of specialized apps.
Furthermore, industry observers have noted the jurisdictional ambiguity of the rule. Because many of these apps are not licensed as telecommunications service providers, they fall outside the traditional purview of the Indian Telegraph Act. The move to bridge the gap between "over-the-top" (OTT) apps and the underlying telecom network raises significant questions about the long-term governance of digital communication tools in India.
AI-Driven Calls and the New A2P Framework
Beyond the mandate for data sharing, the new regulations introduce a robust framework for managing Artificial Intelligence-powered calls. As generative AI becomes increasingly capable of mimicking human speech, the threat of sophisticated, automated, and personalized spam—often referred to as "vishing" (voice phishing)—has reached a new peak.
Under the amended rules, all calls initiated by software or AI voice agents are now classified under the Application-to-Person (A2P) framework. This requires companies to declare their use of such technology to their telecom operators. Any calls made using AI or prerecorded voices that are not pre-registered will be treated as spam and subject to immediate blocking or administrative action.
This is a proactive attempt by TRAI to regulate the "how" rather than just the "what" of modern telemarketing. By mandating transparency, the regulator aims to ensure that if a business uses an AI agent to contact a customer, that call must be traceable to a legitimate, verified entity. To further incentivize compliance, the regulator has allowed telecom operators to impose a termination charge of up to 5 paise per minute on A2P calls, creating a financial barrier to the mass-scale deployment of robocalls.
Implications and Policy Challenges
The implementation of these rules faces several practical hurdles. First, the ambiguity surrounding "what" constitutes a reportable event remains a point of contention. Industry experts like Kazim Rizvi of The Dialogue have noted that there is a massive difference between sharing a single user’s manual "spam" report and sharing an entire proprietary dataset of reputation signals. The regulator has yet to clarify if the rules will extend to the native spam-detection features embedded within smartphone operating systems like Android and iOS. If the mandate applies to third-party apps but not to OS-level dialers, it could create a fragmented enforcement landscape.
Second, the technical standards for data transmission are currently undefined. For an app with 350 million users, pushing real-time spam signals to a blockchain platform requires significant investment in infrastructure and rigorous adherence to data privacy standards. The risk of data leakage or the misclassification of legitimate calls as "spam" on a centralized network could have unintended consequences for the quality of service provided to the end-user.
Finally, the classification of AI-assisted calls remains broad. Experts from consulting firms like The Quantum Hub have pointed out that the current definition of A2P may inadvertently sweep up legitimate business communications, such as calls from contact centers or automated appointment reminders, under the same restrictive banner as spam. Without a clear distinction between high-volume marketing spam and essential service-based communications, the industry fears a chilling effect on business-to-consumer interactions.
The Path Forward
As the regulatory dust settles, the focus now turns to compliance and enforcement. TRAI is expected to issue further clarifications on the technical protocols for data sharing, but the core ideological conflict—the autonomy of private apps versus the regulatory control of the telecom network—appears set to persist.
For the millions of Indians who rely on these apps to navigate an increasingly noisy digital environment, the outcome of this clash is critical. If the new rules succeed, they could create a more secure communication ecosystem where the network itself is hardened against fraud. However, if the requirements are implemented in a way that undermines the technical efficacy of independent filtering tools, users might find themselves facing a new wave of sophisticated spam that the unified, but potentially less agile, state-led systems struggle to catch.
The coming months will likely see legal challenges, further rounds of consultation, and a significant technical overhaul as both the telecom industry and app developers adjust to a landscape where data sharing is no longer voluntary, but a condition of doing business in one of the world’s most dynamic digital markets.




Leave a Reply